Governments and companies around the world are racing to secure websites and online services after the discovery of two critical vulnerabilities in PHP, the widely used programming language that powers a substantial portion of the internet.
The security flaws, identified as CVE-2026-109618 and CVE-2026-109619, can allow an unauthenticated attacker to remotely execute code on vulnerable web servers, potentially giving intruders control over affected systems and exposing sensitive information.
The PHP development team released emergency security updates on October 21, 2026, urging users to update immediately to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, depending on the version being used.
PHP warned that all installations serving web requests could potentially be affected and said there were no complete alternative mitigations, making installation of the security update the safest response.
The vulnerabilities have triggered a global cybersecurity scramble because PHP is deeply embedded in websites and web applications, including content management systems and other platforms used by governments, businesses and organisations worldwide.
WordPress, Drupal and numerous other web platforms rely on PHP to process information and deliver dynamic webpages, meaning organisations may depend on the language even when ordinary users are unaware of it.
OpenAI said the vulnerabilities were uncovered through a coordinated security initiative involving software maintainers, cybersecurity researchers and infrastructure providers.
According to the company, U.S.-based cybersecurity firm Calif identified a critical flaw using OpenAI’s GPT-5.6 Sol model under its “Patch the Planet” initiative, while cybersecurity company Wiz independently discovered and reported both vulnerabilities.
OpenAI described the development as “one of the most impactful security issues in recent memory” because of the severity of the flaws and PHP’s widespread use.
The company said the discovery demonstrated how advanced artificial intelligence could help defenders uncover vulnerabilities with internet-scale consequences, while warning that similar capabilities could also enable attackers to rapidly develop offensive tools after technical details become public.
The PHP maintainers subsequently developed and released fixes, with OpenAI, Wiz, Cloudflare and other security organisations contributing research, technical assistance and coordination ahead of the public disclosure.
However, the race between defenders and potential attackers intensified once information about the vulnerabilities began circulating publicly.
Cloudflare Chief Executive Matthew Prince said the company observed thousands of attempts to exploit the flaws in the hours before the public announcement.
According to Prince, the number jumped to tens of thousands within 45 minutes of disclosure, hundreds of thousands within two hours and eventually millions as attackers began scanning the internet for vulnerable systems.
Amazon also disclosed that its threat-intelligence systems had detected an attempt to exploit the vulnerabilities as early as October 17, four days before the official public disclosure.
Amazon said the attempt targeted its MadPot honeypot infrastructure from an IP address associated with a commercial anonymisation network.
The company said it remained unclear how the actor obtained information about the vulnerability before the planned disclosure.
The developments prompted governments and major companies to take some websites and online services offline as a precaution while security teams applied patches and examined systems for possible compromise.
In Finland, public internet services operated by government authorities were temporarily taken offline while security teams responded to the vulnerabilities.
The Finnish Government ICT Centre said the shutdowns were precautionary rather than the result of a confirmed cyberattack, with services gradually being restored following security updates and testing.
Japan also moved quickly to contain the risk.
Prime Minister Sanae Takaichi urged operators using PHP to prepare to install the security patches immediately and said temporarily suspending vulnerable websites could be an effective protective measure where updates could not be applied quickly.
Japanese government bodies, including the Ministry of Finance, temporarily suspended parts of their online services while security work was carried out.
The Japanese Finance Ministry later said some services were being restored after necessary security measures had been implemented and safety confirmed.
Japanese banks, airlines, railway operators, insurers and other companies also temporarily restricted some online services as they investigated their exposure to the flaws.
France’s telecommunications group Orange similarly suspended access to certain PHP-based websites and applications across some subsidiaries as a precaution.
In China, authorities urged organisations and internet users to inspect their systems and upgrade to secure PHP versions.
Tencent Cloud advised customers to update affected systems, while other technology companies moved to examine their infrastructure and reduce the possibility of server hijacking or data theft.
South Korea also raised its private-sector cybersecurity alert level and activated emergency response measures amid concerns that attempts to exploit vulnerable servers could increase.
The danger stems from the ability of the flaws to permit remote code execution without authentication.
In practical terms, a successful attacker could potentially cause a vulnerable server to execute unauthorised commands, which could expose data, alter websites or allow further compromise of the affected system.
The problem is particularly serious because PHP operates on web servers rather than on ordinary users’ phones or computers.
For individual internet users, therefore, the immediate concern is less about updating their personal devices and more about whether the organisations handling their information have secured their servers.
Users may nevertheless encounter temporary outages involving government portals, banking platforms, commercial websites and other online services as operators take systems offline for patching and security testing.
Security experts have cautioned that restoring complex systems could take time, particularly for smaller organisations running older PHP versions or infrastructure that has not been regularly maintained.
The crisis also highlights the increasingly important role of artificial intelligence in cybersecurity.
While AI systems can help researchers identify vulnerabilities more quickly and allow software developers to prepare fixes before attackers discover them, the same technology could potentially help malicious actors analyse disclosed weaknesses and automate attacks across large numbers of targets.
For website operators, PHP’s own guidance remains clear: affected systems should be upgraded to the patched releases immediately.
With scanning and attempted exploitation already occurring on a massive scale, security agencies and technology companies are urging organisations not to delay updates and to investigate their systems for signs of compromise.
Although the surge in exploit attempts does not mean that every attempt succeeded, the scale and speed of the activity have placed governments, businesses and cybersecurity teams worldwide on heightened alert as they work to secure one of the internet’s most widely used software foundations.
[A MUST HAVE] Evidence Act Demystified With Recent And Contemporary Cases And Materials
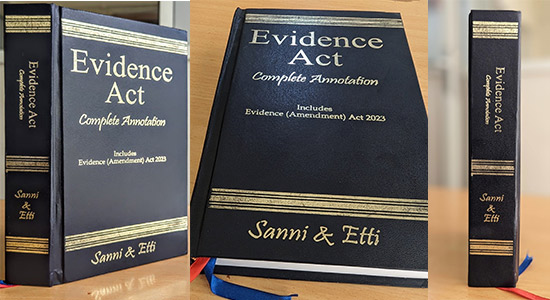
Available now for NGN 40,000 at ASC Publications, 10, Boyle Street, Onikan, Lagos. Beside High Court, TBS. Email publications@ayindesanni.com or WhatsApp +2347056667384. Purchase Link: https://paystack.com/buy/evidence-act-complete-annotation
______________________________________________________________________ “Enhance Legal Practice With Authoritative Reports” — Alexander Payne Offers Comprehensive Law Reports, Spanning Over A Century Of Nigerian Jurisprudence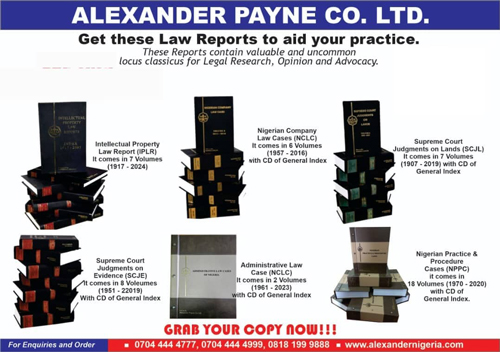 Interested buyers are encouraged to place their orders and enquiries via:
0704 444 4777, 0704 444 4999, 0818 199 9888
Website: www.alexandernigeria.com