
*Places enormous responsibility on board of directors, others
The Central Bank of Nigeria (CBN) yesterday moved to strengthen cyber resilience of Other Financial Institutions (OFIs) under its regulation in order to ensure that they remain safe and sound amidst increase in the number and sophistication of cybersecurity threats and attacks against them.
The move was contained in a circular titled, “Exposure Draft of the Rise-Based Cybersecurity Framework and Guidelines for Other Financial Institutions” which was addressed to all OFIs in the country.
The CBN correspondence dated August 13, 2021, and signed by the Director, OFIs Department, Nkiru Asiegbu, stipulated the minimum requirements for enhancing cybersecurity.
The apex bank explained that the purpose of the guidelines which provides a risk-based approach to managing cybersecurity risk, was to among other things create a safer and more secure cyber environment that supports information system security and promote stability of the OFI sub-sector.
It noted that the safety and soundness of the sub-sector particularly required that they operate in a safe and secure environment.
Hence, it stated that the platform on which information processed and transmitted should be managed in a way that ensures the confidentiality, integrity and availability of information as well as the avoidance of financial loss and reputational risk among others.
Essentially, the document provided for cybersecurity governance and oversight; cybersecurity risk management system; cyber resilience assessment; cyber operational resilience; cyber threat intelligence and metrics monitoring and reporting.
The guidelines also spelt out the responsibilities of the board of directors, senior management and chief information security officer (CISO).
The CBN stated that the board of directors shall ensure that cybersecurity is completely integrated with business functions and as well managed across the OFI.
The board is also to have oversight and overall responsibility for cybersecurity programmes.
In addition, senior management of OFIs be responsible for the implementation of the board approved cybersecurity strategy, policies, standards and the destination of cybersecurity responsibilities among others.
The document also mandated every OFI to appoint or designate a CISO whose responsibilities shall include the day to day cybersecurity activities and the mitigation of cybersecurity risks in the institution.
[A MUST HAVE] Evidence Act Demystified With Recent And Contemporary Cases And Materials
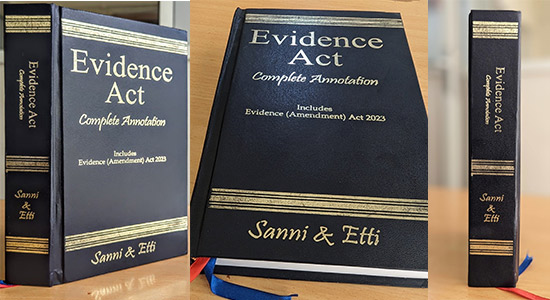
Available now for NGN 40,000 at ASC Publications, 10, Boyle Street, Onikan, Lagos. Beside High Court, TBS. Email publications@ayindesanni.com or WhatsApp +2347056667384. Purchase Link: https://paystack.com/buy/evidence-act-complete-annotation
______________________________________________________________________ “Enhance Legal Practice With Authoritative Reports” — Alexander Payne Offers Comprehensive Law Reports, Spanning Over A Century Of Nigerian Jurisprudence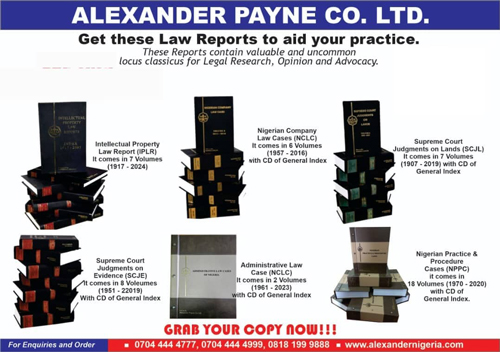 Interested buyers are encouraged to place their orders and enquiries via:
0704 444 4777, 0704 444 4999, 0818 199 9888
Website: www.alexandernigeria.com